




This is our heartfelt blog on #OWASPSeasides (a free to attend hacking conference in Goa). As many of you must be aware of it, since more than a decade, OWASP has been a community that produces freely-available articles, methodologies, tools, and technologies in the web application security. OWASP Seasides is first of its kind to provide the free training, workshops and talks to the participants.
We started the OWASP Seasides with the thought that we will try to provide training to some 150+ people but the way it grew, participants count crossed 400+. Initially, we had only a couple of training on paper but we eventually ended up with 7 training with 3 villages and a CTF. The response from the participants was absolutely overwhelming. It was a great learning experience for us as a team in how to organise the conference, what could go wrong and how to manage it on the fly.
A lot of our attendees actively engaged with us on social media and it became this never-ending string of fun memes and videos to promote the conference. We joked about the resemblance we felt between making a movie and organising this conference.
Thus we ended up making this trailer for Seasides, Gangs of Seasides — https://www.youtube.com/watch?v=0_4bfq_77X0
As many of us can relate, the first conference we attend turns out to be overwhelming for being around some of the best security researchers in the world, being able to meet them and have their valuable advice. Nothing short of a goldmine, to say, for many of us who were getting started with hacking and trying to make a career in InfoSec.
First Day stated with the wonderful workshops and Village. While discussing technology, it’s only fair we include Blockchain and Machine Learning. Industry’s best speakers came to give a kickstart on Machine Learning and Blockchain.
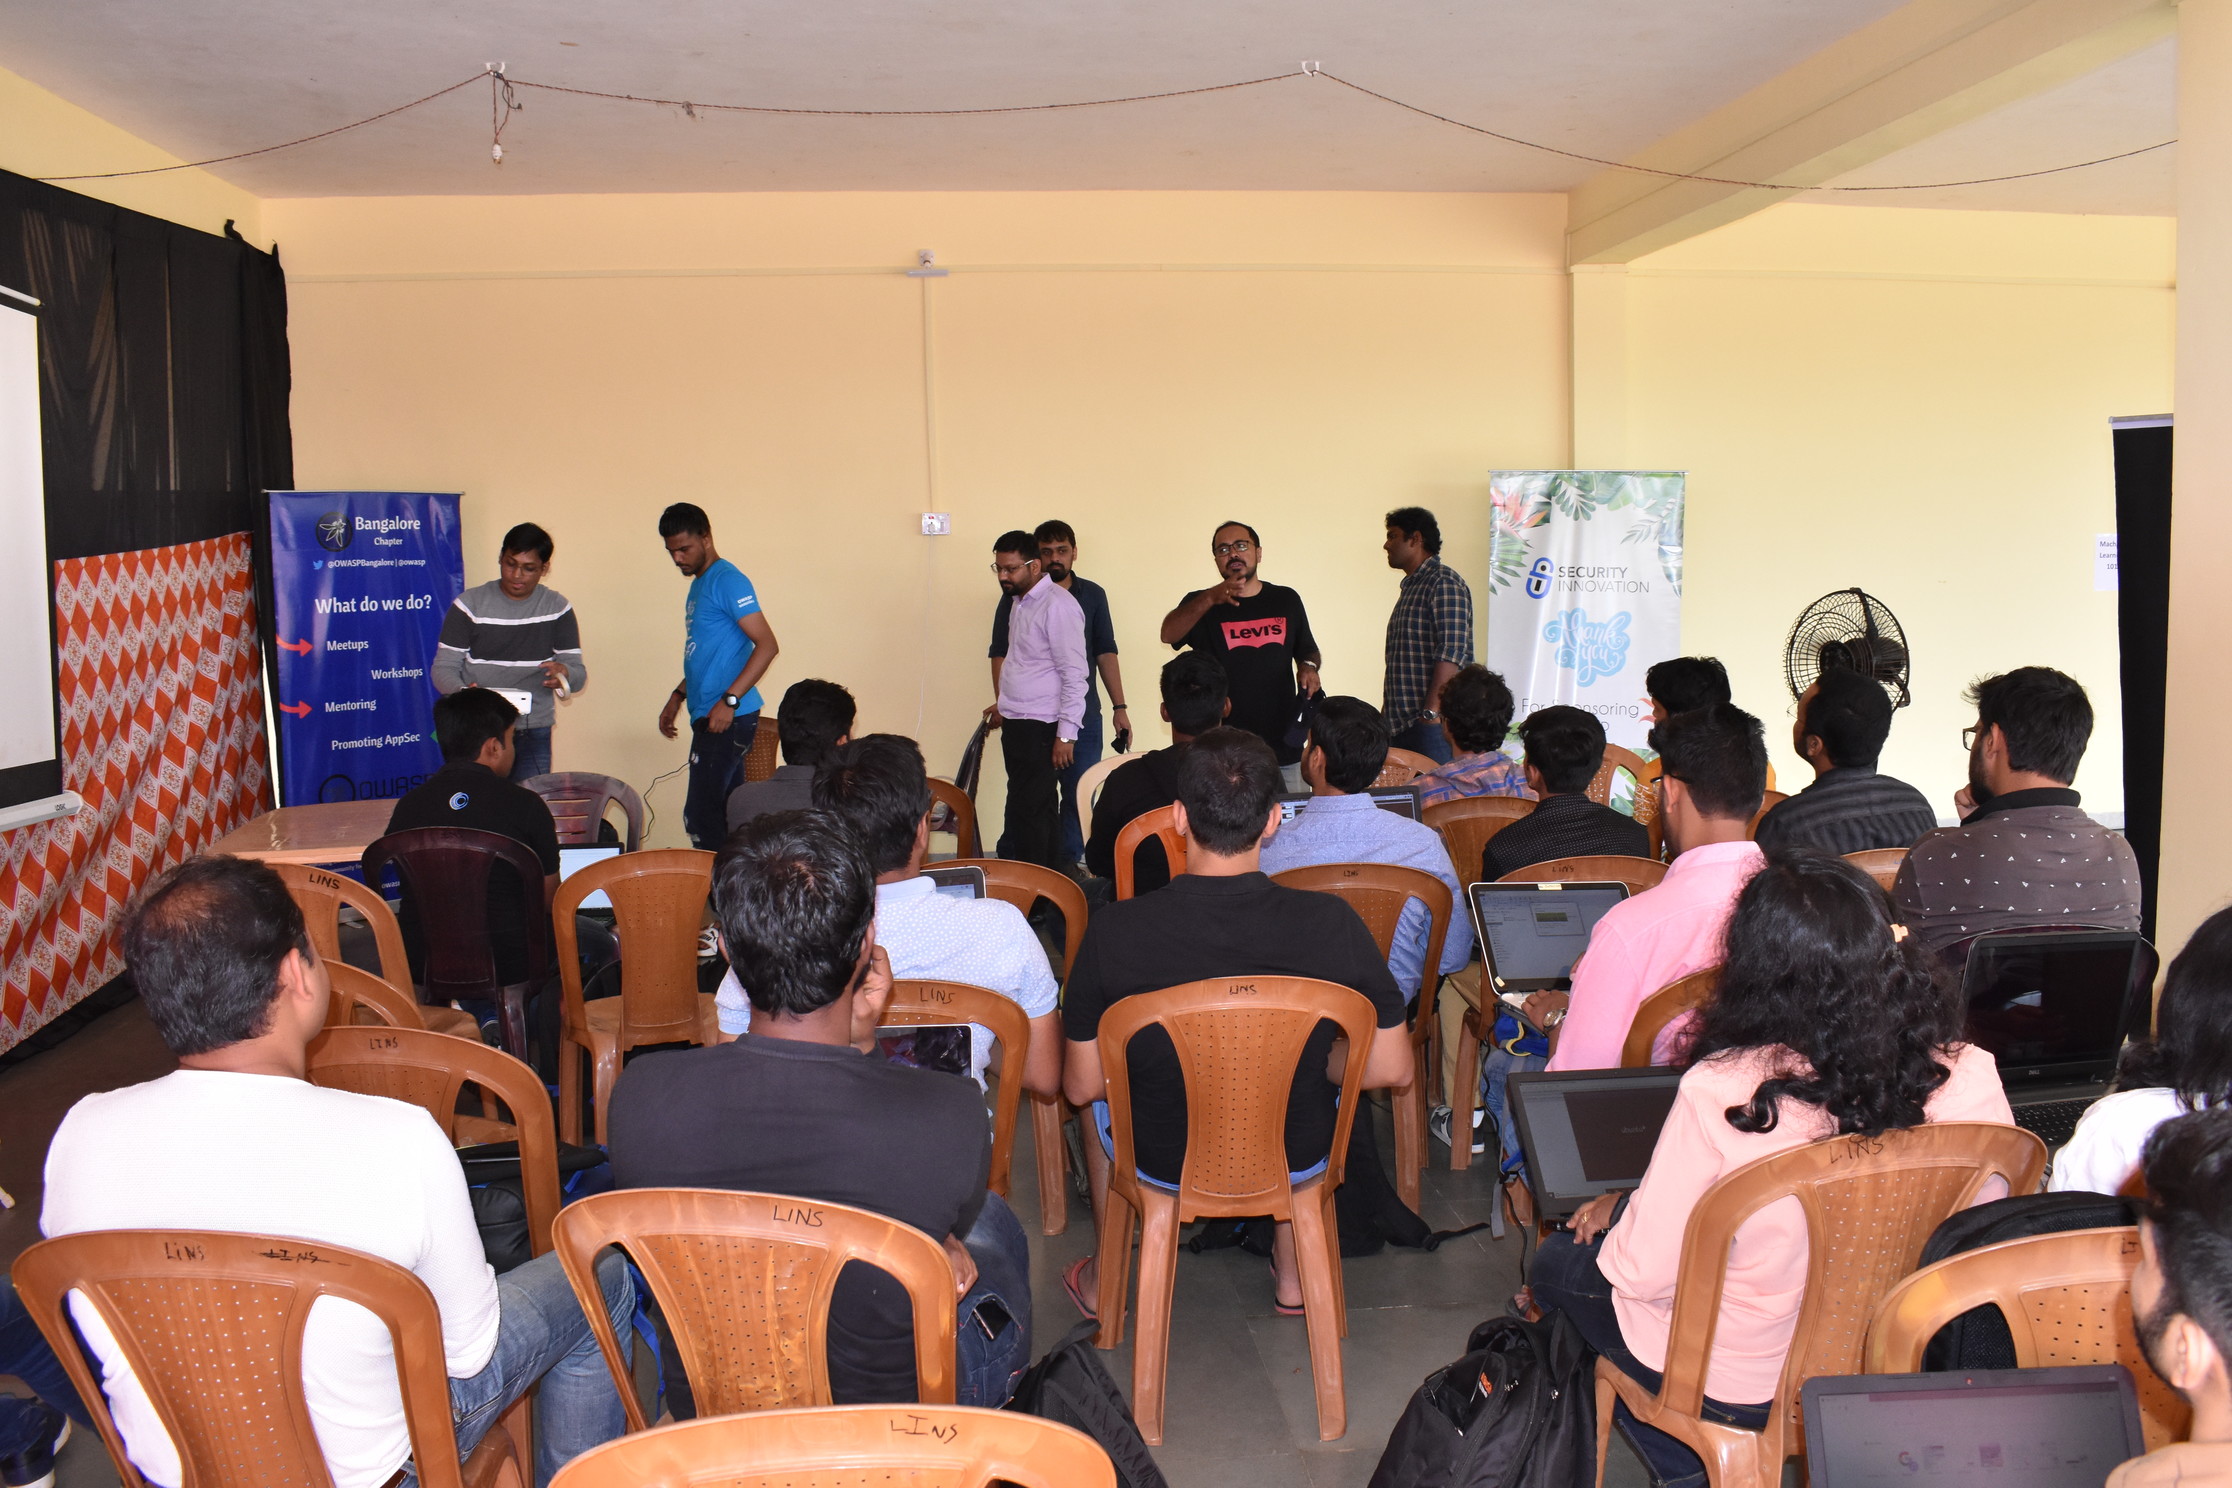
- Learning Secure Development from Blockchain — Blockchain Village
- Red teaming village, you can team up and play CTF in exciting real world scenarios
- The Event had a web application pen-testing training for Women which was given by women and volunteers were also women. Over 25 women joined us for the training and discussions with them were very engaging. Out of 25, few were college students from different parts of the country. The full-day training went on really well. Jason Haddix and Chloe joined us after the training session. Jason Haddix (VP Bugcrowd) mentioned he will be giving his unique Bug Hunter Methodology training to the ladies over zoom for free.
- Android and iOS app Pentesting Workshop
- Car hacking village was one of the amazing place wherein Trainer rented the car very same day and showed the participants how to hack it. Attendees were super thrilled for hands-on car hacking village.
- With the help of Bugcrowd, we provided a full day workshop on Bug Hunters Methodologies by Jason Haddix which experienced meteoric footfall.
- We had a workshop on how to set up security automation in CI/CD pipeline.
We wanted to push forward hardware hacking so we started with soldering village this year and taught basic electronics and soldering with creative electronic Bee hardware inspired from OWASP logo. The village had phenomenal response and our machines kept running non stop all day long.
- We also had elaborately discussed OWASP Top 10 vulnerabilities hands-on.
Apart from the training, we also organised a special dinner for the ladies wherein over 40 ladies joined us. It was amazing to know and talk to all the ladies at one table. I am attaching pictures from the event. During Our Dinner over 40 women joined us. Thanks to #BugCrowd for their kind Gesture for sponsoring the dinner.
We had amazing talks and panel discussion in the evening on 27th and 28th February.
Day 1 — Panel Discussion on Entrepreneurship
Evening Talks by the wonderful speakers
- We have Security with smart contracts
- Talk on Car Hacking Nowadays by Henrik Noelscher.
- The other side of bug bounty program
- How I bought my car in 4 days of bug hunting
- Fixing the internet’s auto-immune problem: Bilateral Safe Harbor for good faith Hackers
Day 2 — Panel discussion on the future of Bug Bounty and talks.
Evening Talks by the wonderful speakers
- Detecting and fighting identity frauds using Behavioural Biometrics”
- Making web secure by design
- Building your hacker blackbox for fun and profit
- Leveraging certificate transparency to automate monitoring of new sub domains for fun and profit
- Bringing Left Shift Security change in India E-Market #Bugbounty
Tools Showcase
- https://www.owaspseasides.com/tools-showcase/day-1-27-feb-2019
- https://www.owaspseasides.com/tools-showcase/day-2-28-feb-2019
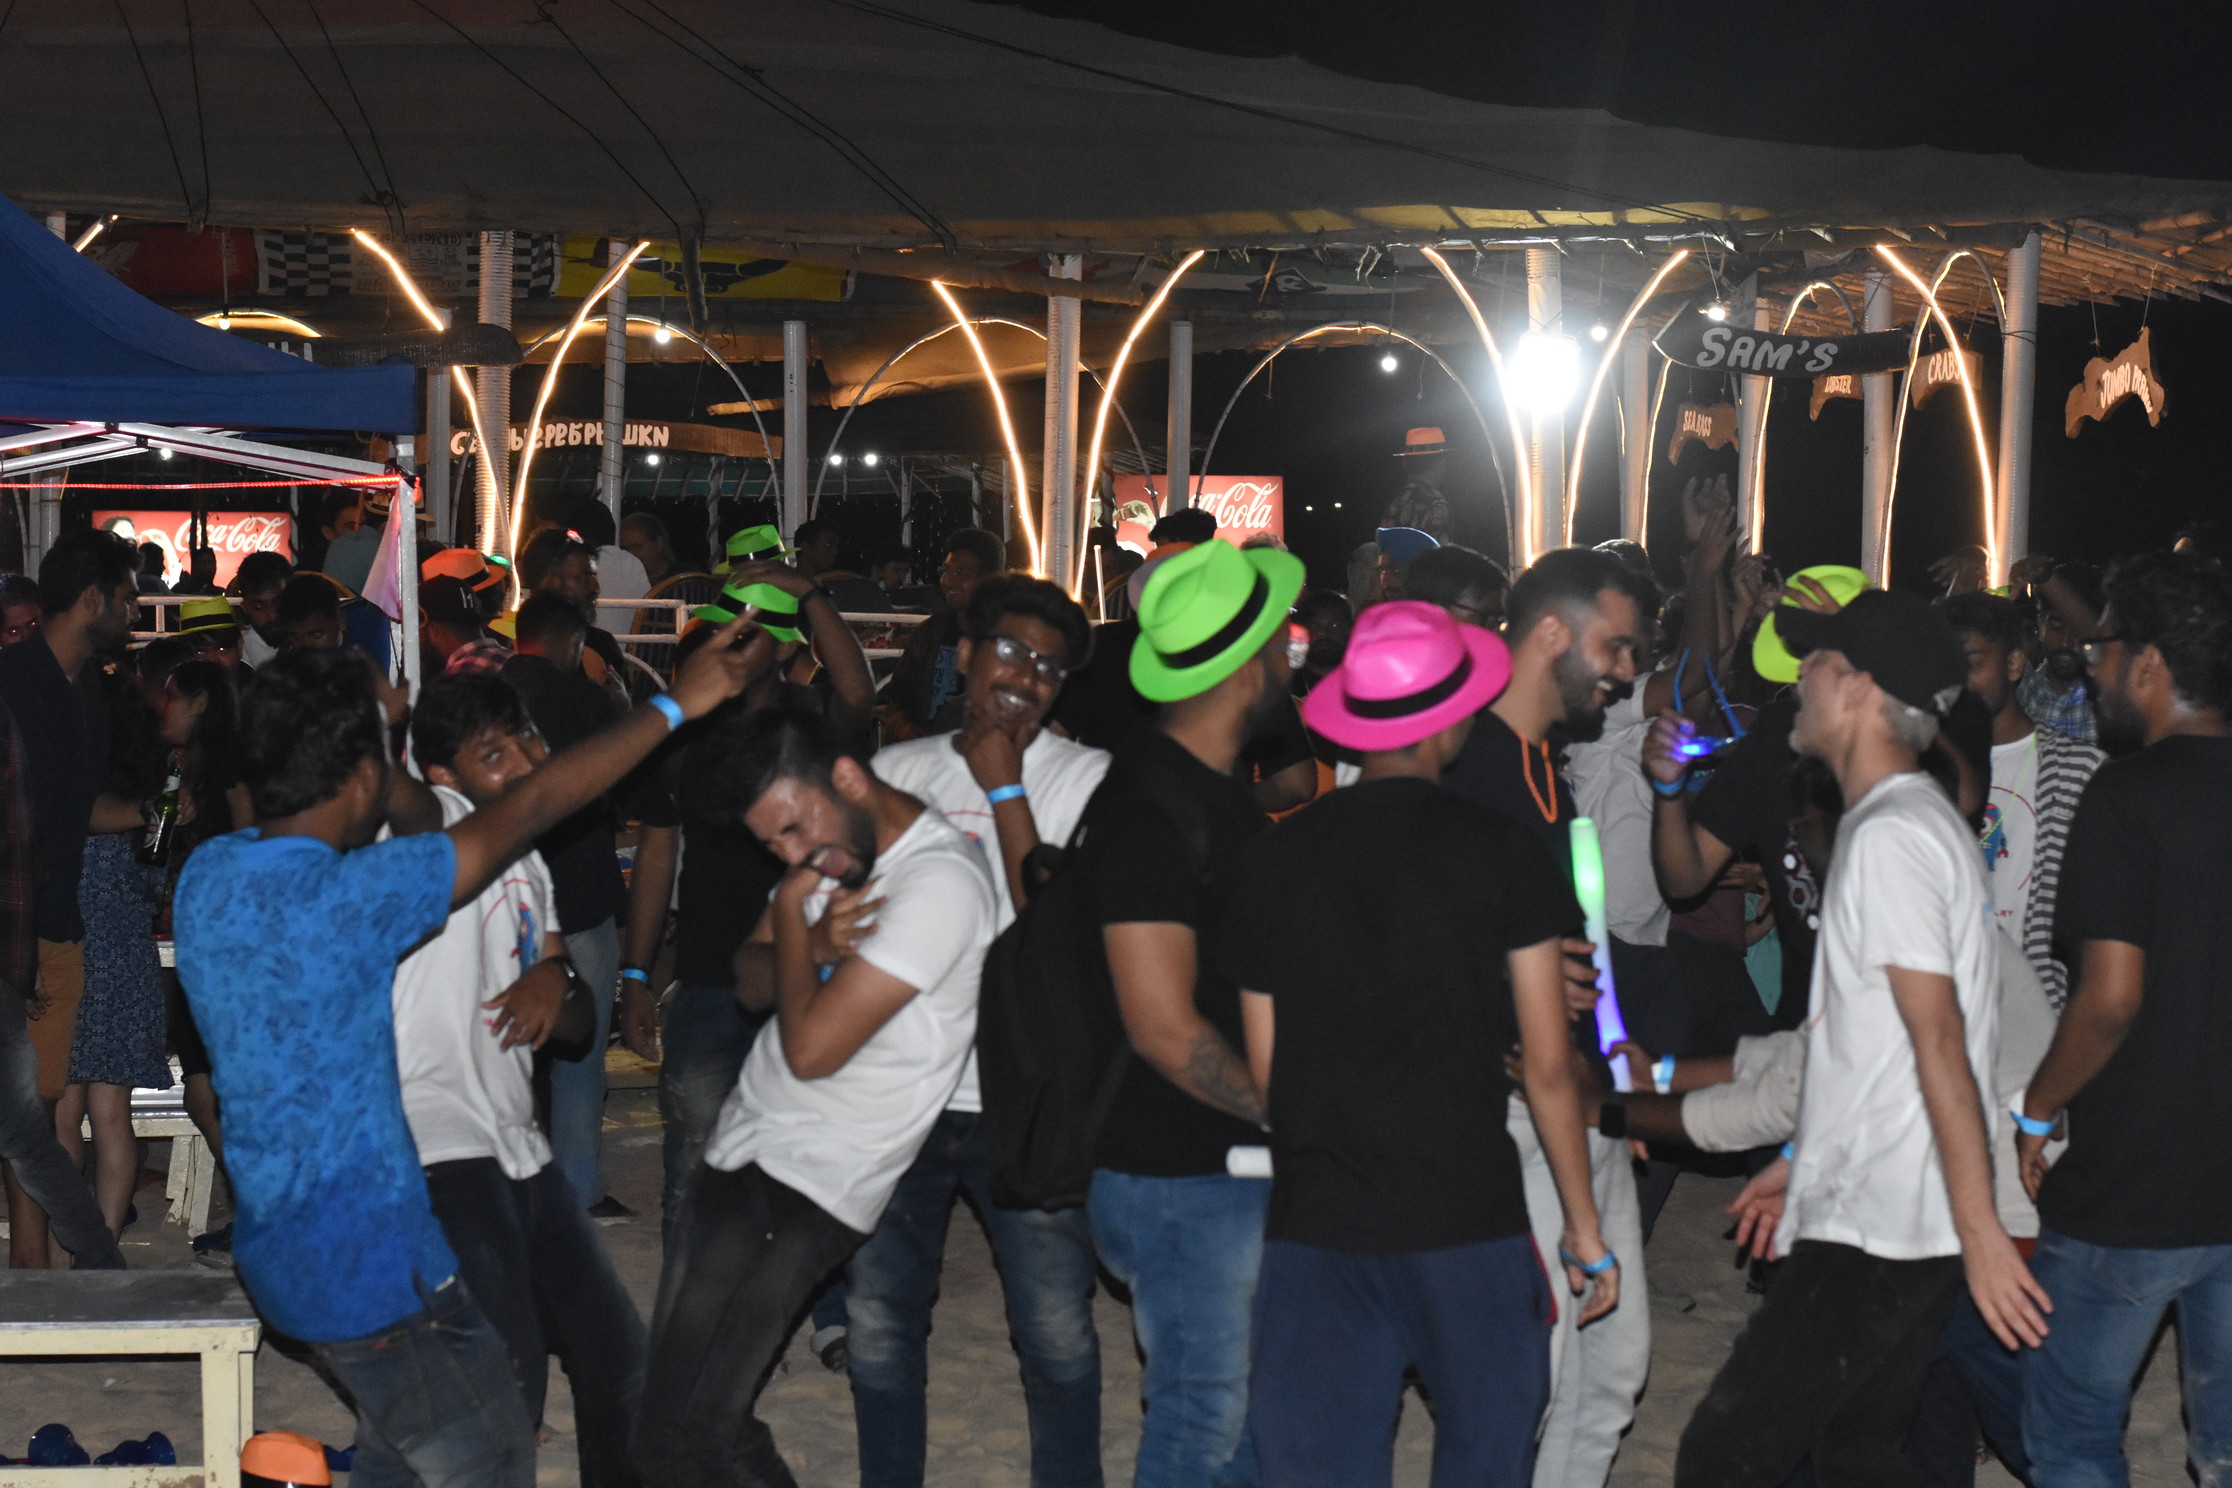
To wrap the conference, we had a wonderful party with our DJ as Arun Mane (The car hacker).
Finally, this conference wouldn’t come to reality if we did not have the massive support from our sponsors. From the venue, luncheon, swags, logistics and everything else — we got to experience love and support from our sponsors who made it possible to make this conference free for everyone and they all are our heroes — Bugcrowd, Avatao, Anlyz, Security Innovation, Bug Bounty World, Peritus, Secmasters, We45, Intouch world, Cloudsek, Enciphers and many kind-hearted individuals who gave scholarship for attendees.
Everyone in the volunteer team worked relentlessly to make this conference a success and looked after various tasks at the conference.
Our goal was to organise a conference that’s entirely free to attend while not compromising on any quality whatsoever. So was our response with so many attendees coming over — for a lot of them, Seasides was the first security conference they attended that they absolutely loved the experience.
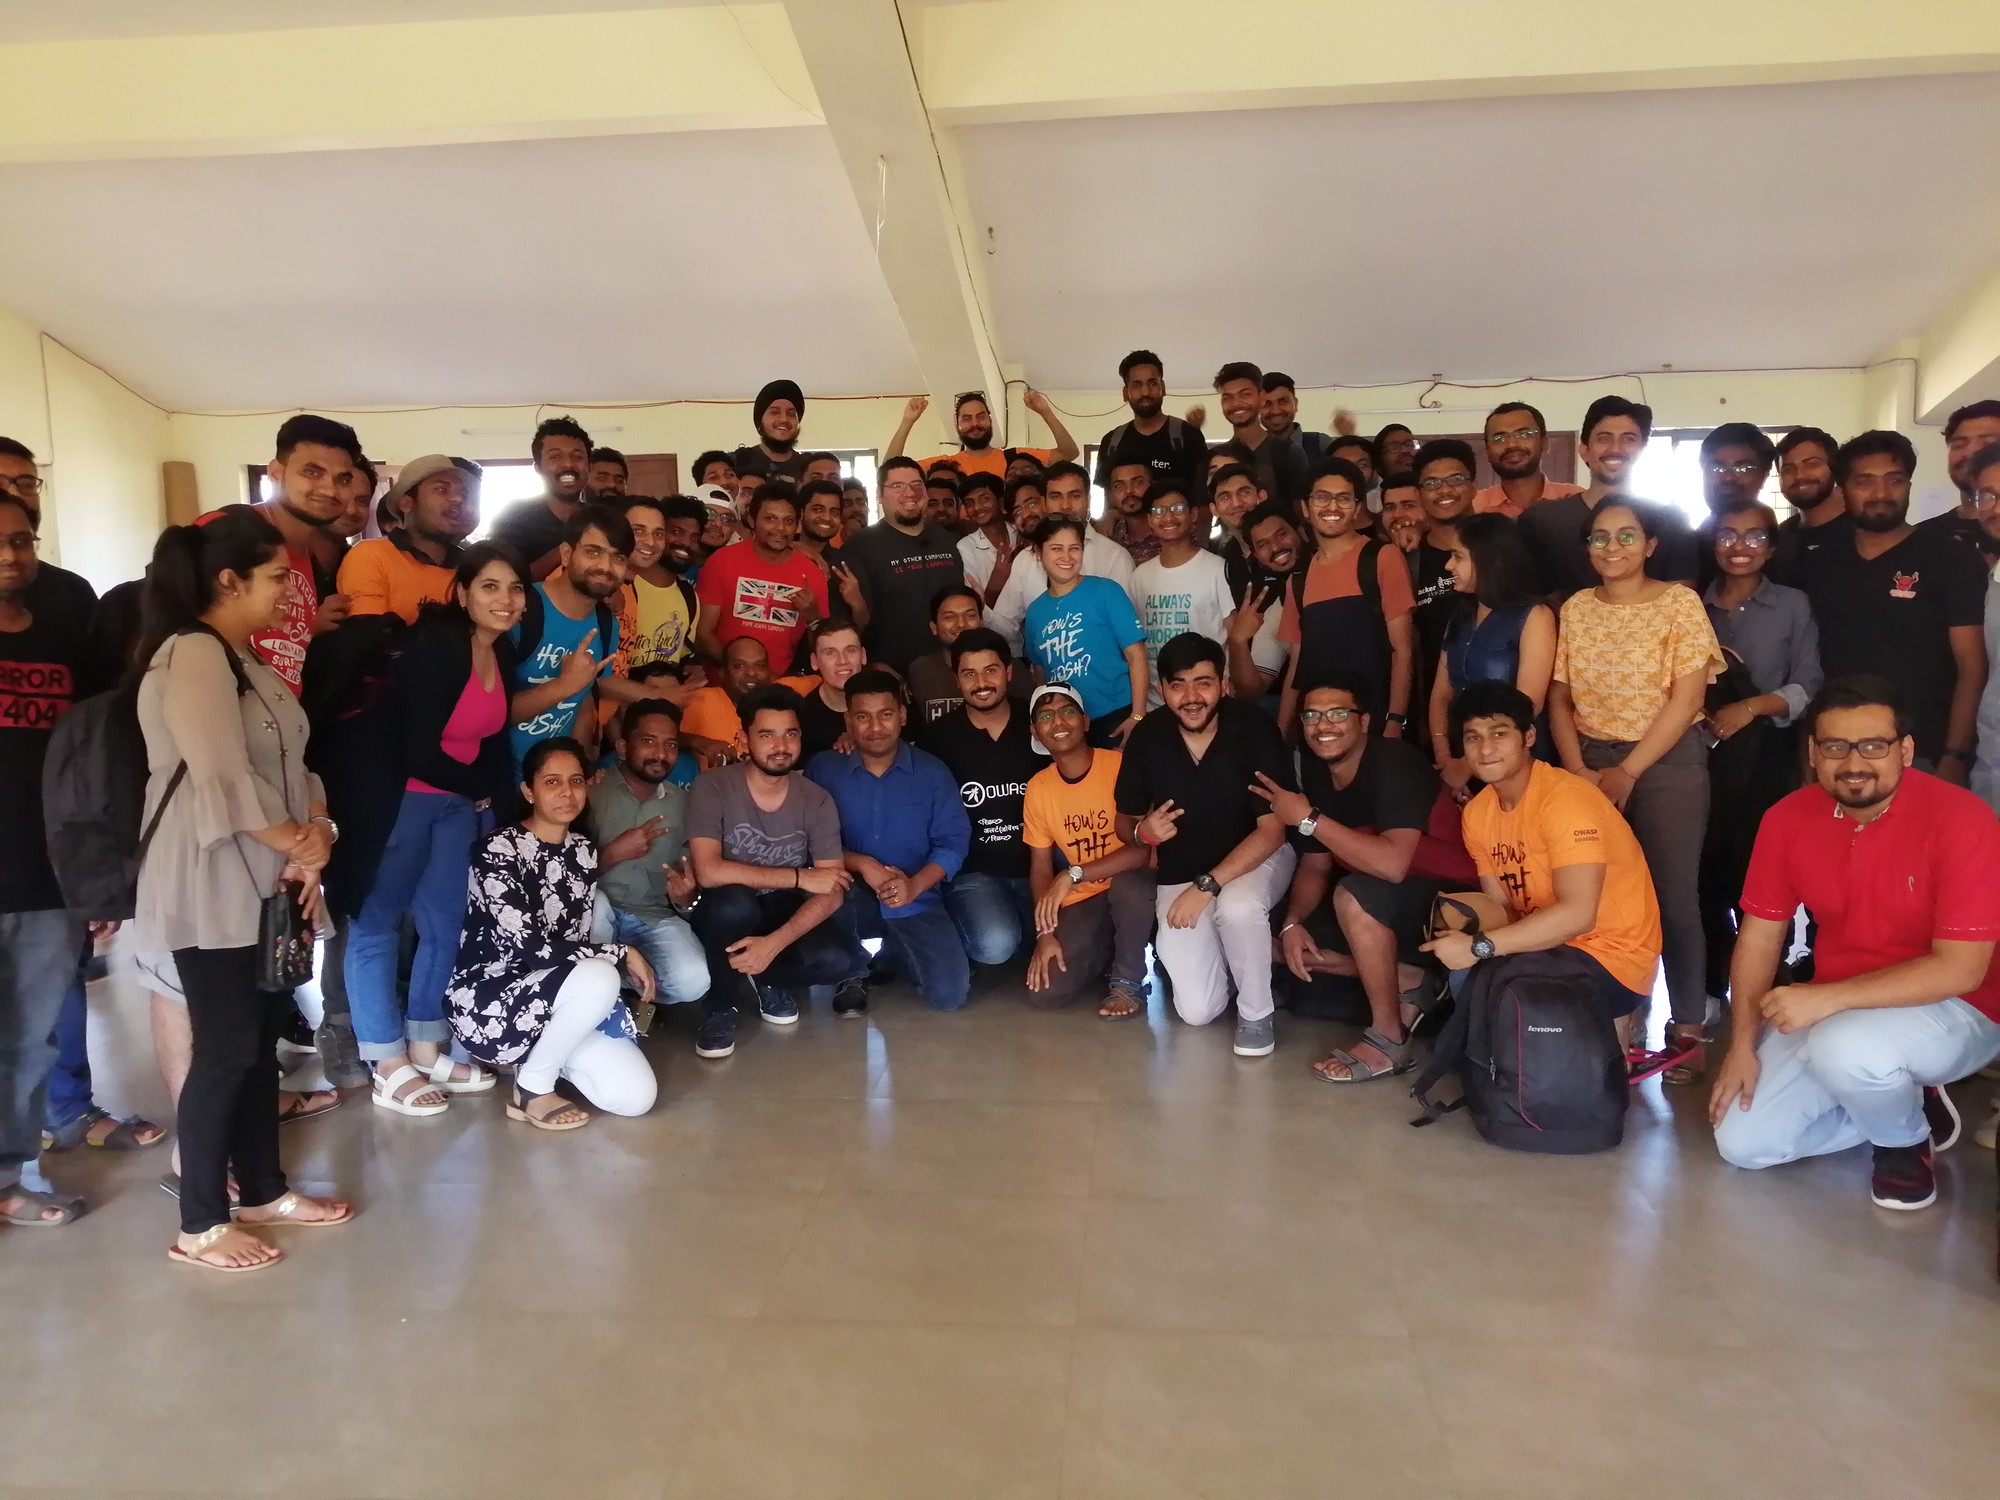
We are deeply grateful for everyone who attended and associated with the conference and cannot wait to begin everything again next time.
Sincerely,
Abhinav SP, Vandana Verma, Prashant KV, Parveen Yadav & OWASP Seasides Team.