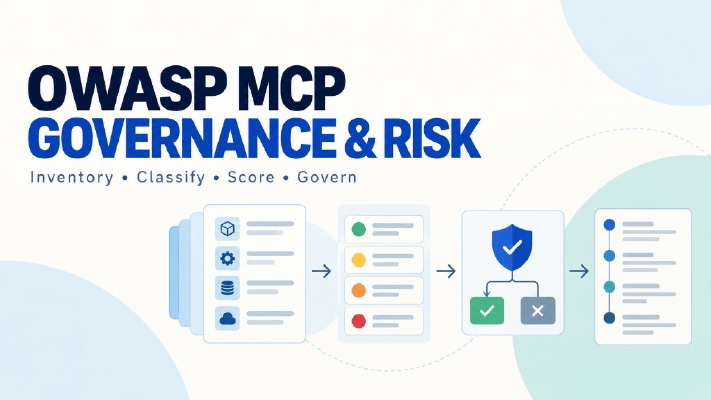
🚀 What it does: A practical framework for deciding whether MCP servers should be allowed in an organization and which controls they require.
The OWASP MCP Governance & Risk Framework helps organizations decide whether an MCP server should be allowed in their environment and under what controls.
The framework provides guidance for asset inventory, ownership, Tier 0–4 server classification, risk scoring, least privilege, meaningful human approval, production logging, evidence collection, and phased rollout.
It also maps controls to the OWASP MCP Top 10, OWASP Top 10 for LLM Applications, NIST AI RMF, ISO/IEC 42001, and SOC 2 to support security architecture, GRC, engineering, and procurement teams.